COMPLIANCE HUB
End-of-life software compliance: requirements and how to comply
Regulations and compliance standards regularly ask “who patches it?” Can you answer?
PCI DSS, HIPAA, SOC 2, FedRAMP, the EU Cyber Resilience Act. Different standards and requirements, but the same question about the end-of-life software you run. When upstream support ends, see why HeroDevs becomes the obvious answer (with the evidence attached).
How end-of-life software becomes a potential compliance violation
Unsupported software risks follow the same three steps every time.
STEP 1
Upstream support ends
The maintainers ship a final release and move on. Your app doesn’t.
STEP 2
A CVE lands
The fix exists for new versions.
Not yours.
STEP 3
Compliance standards ask “who maintains it?”
You don’t have a name, a date, or a document.
As AI scales, compliance requirements expand
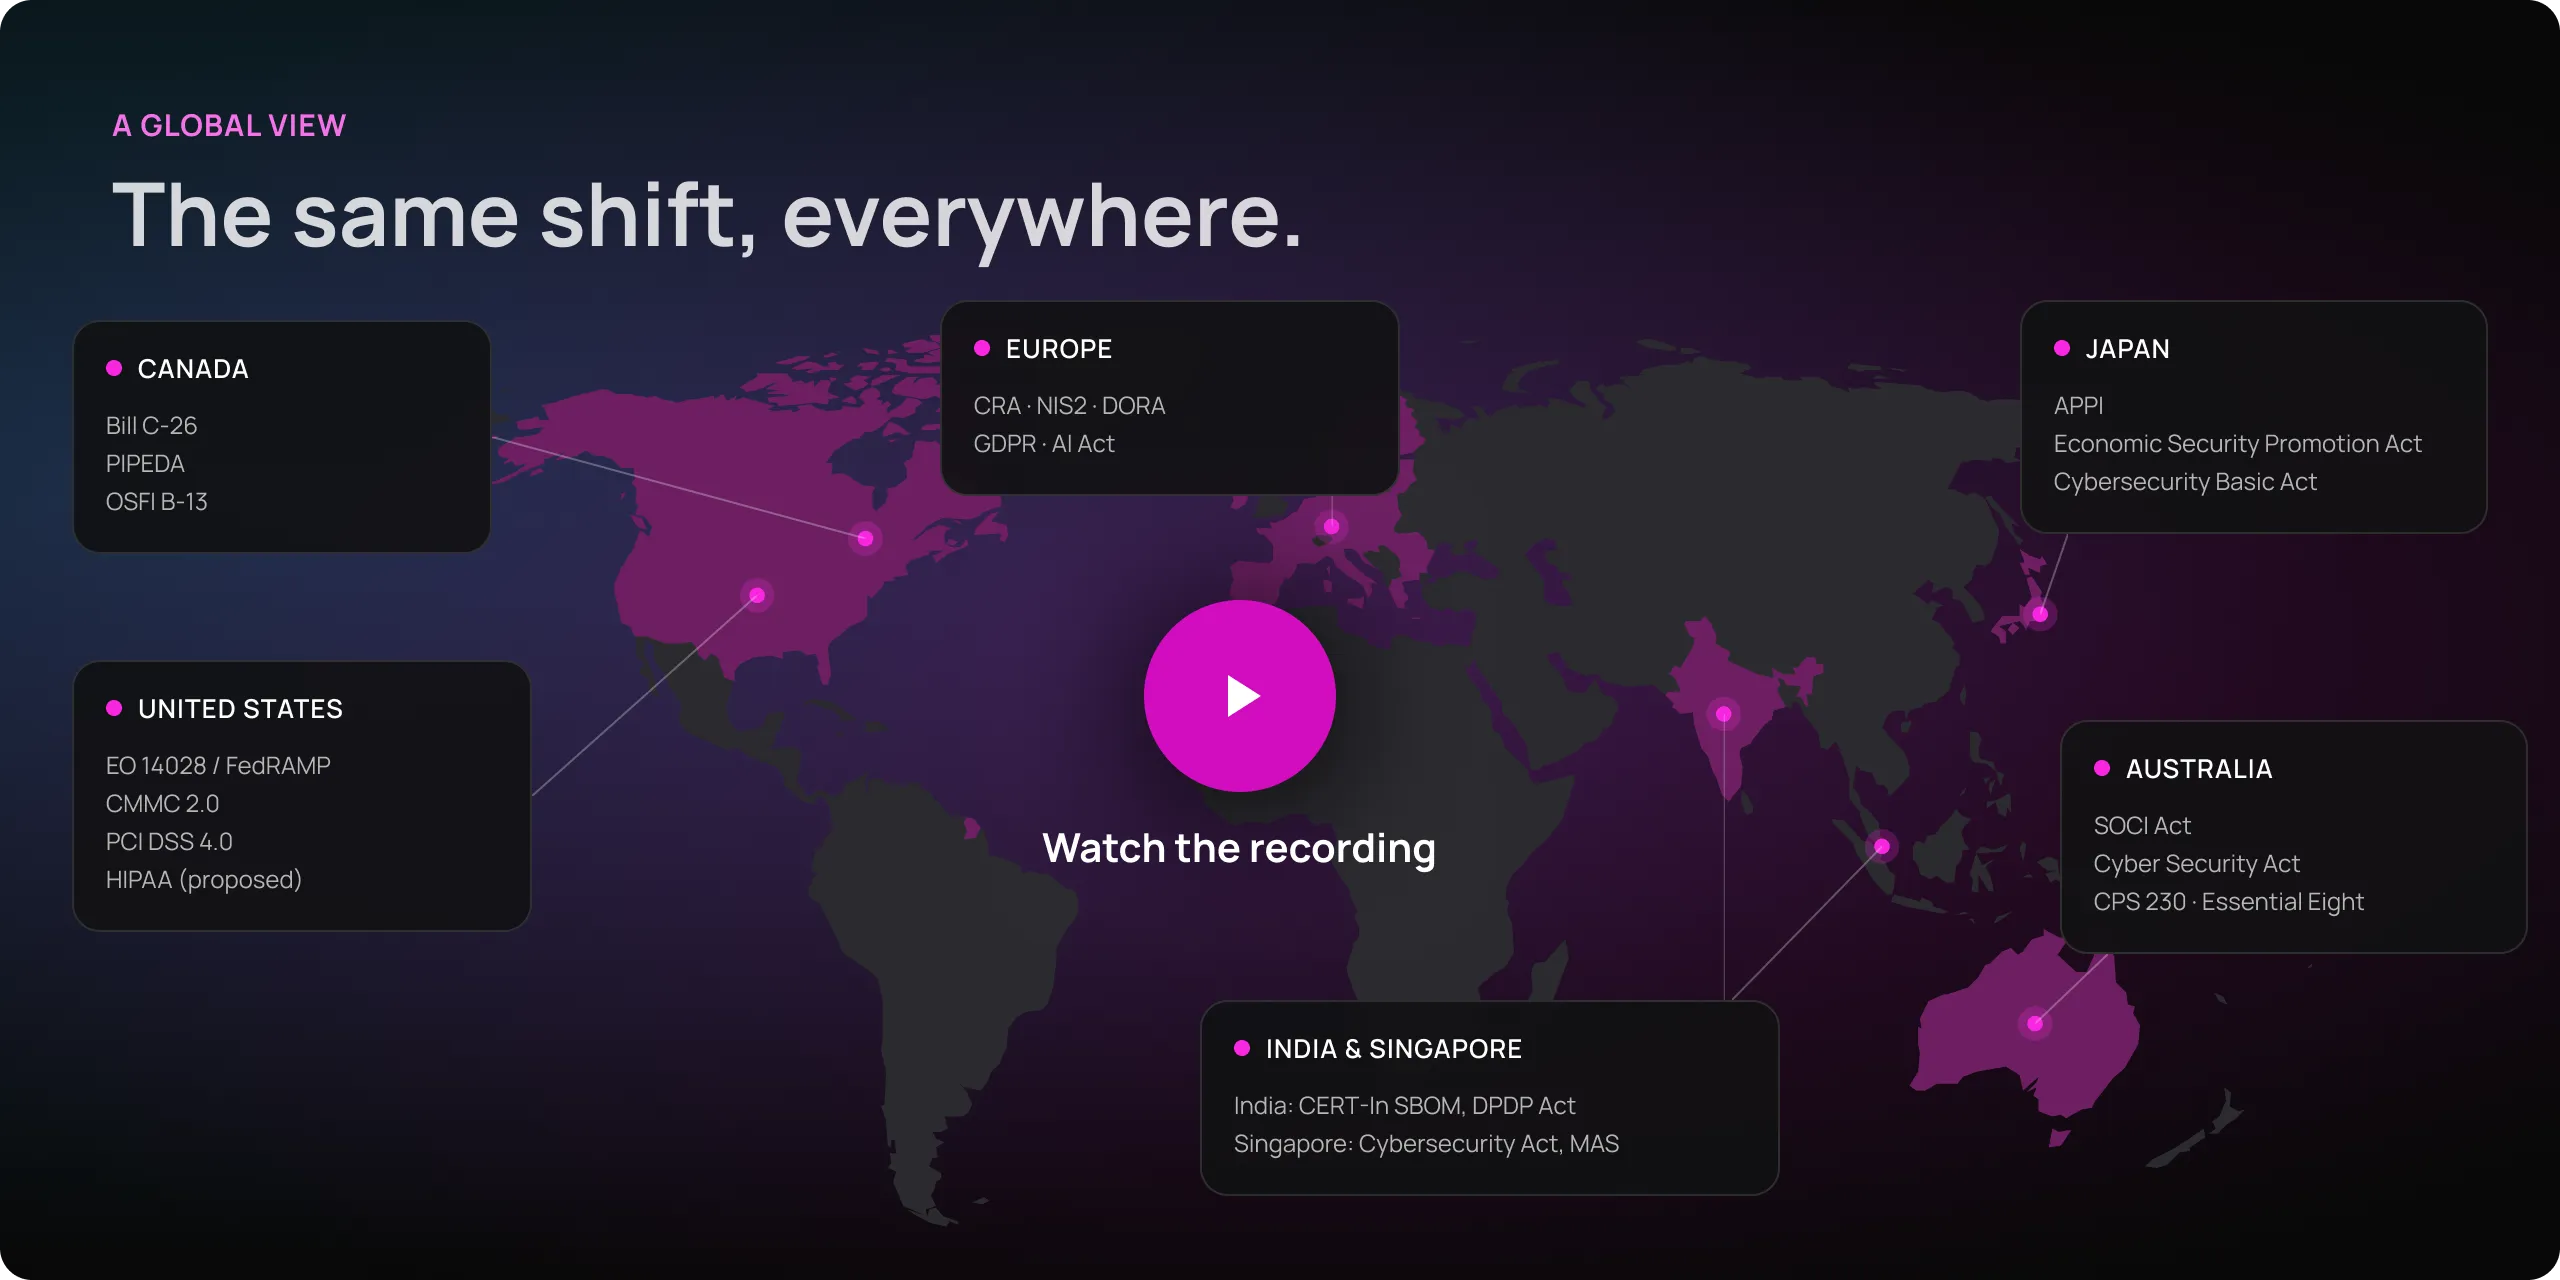
AI is finding and shipping code faster than maintainers can secure it, and regulators worldwide are responding. See how CRA, NIS2, DORA and more turn best-effort security into an evidence-backed obligation for the end-of-life open source you run.
Find your end-of-life open source before a breach.
EOL exposure report
Every end-of-life dependency across your repos, direct and transitive. The same list an assessor would build.
CRA readiness check
16 questions, about 4 minutes, each tied to the text of the regulation. See your score and what to fix first.

EOL DS for Enterprise
End-of-life detection across every team and repo, with CI/CD enforcement.
What compliance frameworks require for EOL software
Compliance for each regulation may look slightly different. Pick those that apply to you and learn how HeroDevs enables compliance.




Did an audit find EOL software?
Resolve it

HeroDevs Never-Ending Support: The continuous CVE remediation you need
HeroDevs maintains the end-of-life open source you already run, with continuous vulnerability management and the paperwork to prove it.
Drop-in patched releases
Same version line, same public API, CVEs fixed. A config change, not a migration.
14-day CVE SLA
In your contract, so “who patches this, and how fast?” has a written answer.
VEX statement with every fix
Shows which CVEs are fixed or don’t apply, in a format scanners and reviewers accept.
Signed attestation with every fix
Mapped to the frameworks you already report against.
CVE Numbering Authority
Vulnerabilities are confirmed, fixed and disclosed through the official CVE program.
Why compliance-heavy teams choose HeroDevs
19M+
package versions tracked
1,000+
vulnerabilities remediated
1,000+
enterprise customers
“In healthcare, disruption for its own sake isn’t innovation—it’s dangerous.”
— ViTel Net
✓ 100% remediation of known AngularJS vulnerabilities, no migration
Read the story →
“We needed to maintain a secure, compliant application while strategically planning a modernization effort without disrupting our business operations.”
— Energy & sustainability marketplace
✓ Kept SOC 2 and enterprise security requirements in place
Read the story →
“The application was functioning perfectly, but we had a ticking time bomb from a security perspective.”
— Sanlam Private Wealth
✓ 100% framework remediation, aligned with regulatory requirements
Read the story →