Featured Posts


All Posts



Security
Sep 8, 2026
CVE-2026-34486: Apache Tomcat EncryptInterceptor Fail-Open Bypass
How a one-line refactor moved cluster-message decryption from fail-closed to fail-open, letting an unauthenticated attacker reach Tomcat's Java deserialization path on port 4000.
Greg Allen
Share this post via:



Compliance
Sep 8, 2026
Ingress NGINX Is End of Life: How to Keep It Secure on AWS With NES
If you run EKS, AWS's managed Kubernetes offering, there is a good chance Ingress NGINX still sits in your production traffic path.
Justin Gorny
Share this post via:

Security
Sep 7, 2026
Node.js CVE Round-Up: 11 New Vulnerabilities Affecting EOL Node.js 20
HeroDevs patched all eleven vulnerabilities across end-of-life (EOL) Node.js 12–20
Javier Perez
Share this post via:

Migration
Sep 2, 2026
Upgrade or Buy Extended Support for an EOL Framework: How to Decide
Migration and extended support are not opposites. A simple framework for deciding which one fits your timeline.
Maria Spano
Share this post via:

EOL Software
Aug 31, 2026
Drupal 7 End of Life: What It Means and What to Do Now
Drupal 7 has been end-of-life since January 2025, with new module vulnerabilities still surfacing every month.
Javier Perez
Share this post via:
EOL Software
Aug 28, 2026
Running Node.js 20 on AWS: What Deprecation Actually Means and What Your Options Are
Navigating AWS Deprecation Policies and Securing Legacy Runtimes Beyond EOL
Javier Perez
Share this post via:
Security
Aug 28, 2026
Apache Log4j Versions, EOL Dates, and Latest Releases (August 2026)
A complete reference for every Log4j release line, the Log4Shell retrospective, and the seven CVEs disclosed since December 2025 that stop at Log4j 2.25.x.
Greg Allen
Share this post via:
Compliance
Aug 28, 2026
Does Running EOL Software Violate PCI DSS, HIPAA, or SOC 2?
EOL software is not an automatic violation, but it lands on the wrong side of the controls these frameworks enforce.
Rob Nalen
Share this post via:
Compliance
Aug 27, 2026
Six Reasons Why Low-Severity CVEs Become High Risk
AI-driven vulnerability landscape rewrites triage math, especially for end-of-life (EOL) software.
Javier Perez
Share this post via:
Security
Aug 27, 2026
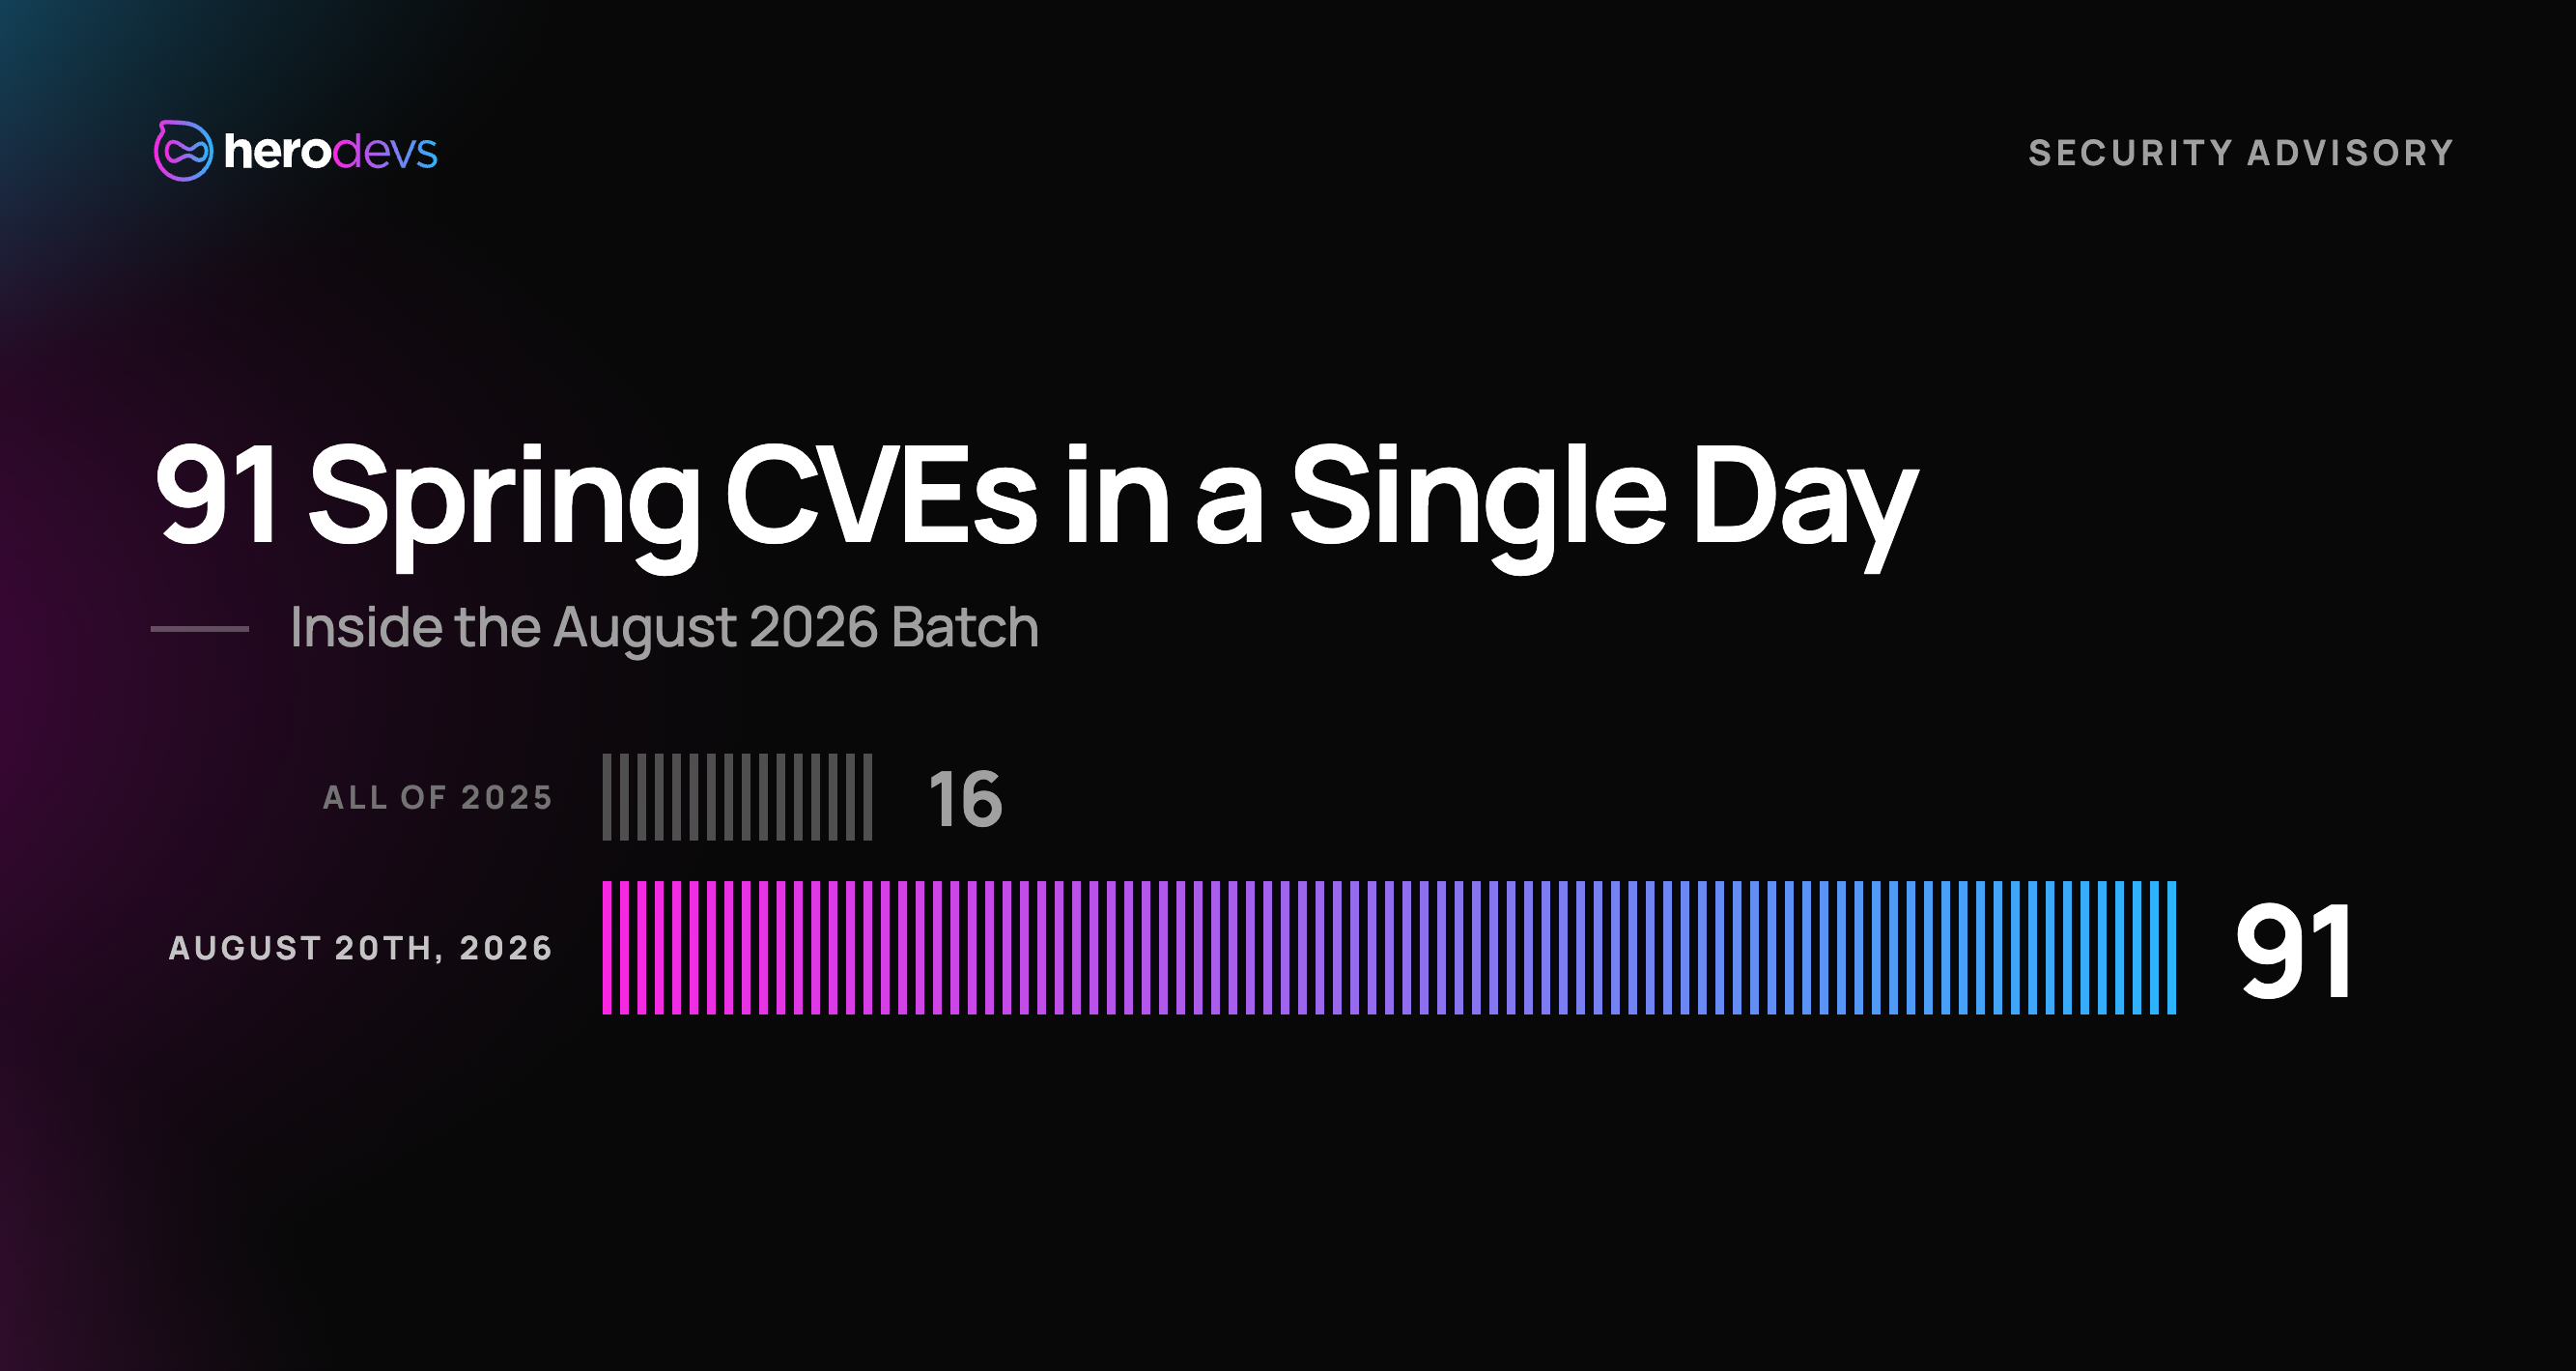
91 Spring CVEs in a Single Day: Inside the August 2026 Batch
Understanding the shift in Spring project security disclosures and what this record-breaking batch means for your Java dependency tree.

Mark Szymanski
Share this post via:
Security
Aug 26, 2026
Apache Tomcat 9.0.121 Fixes 11 CVEs, 8 Affect EOL Tomcat 8.5
How the August 2026 Tomcat security release leaves eight unpatched vulnerabilities, four rated Important, on end-of-life Tomcat 8.5.
Greg Allen
Share this post via:
Security
Aug 26, 2026
AryStinger Explained: How Decade-Old Router Bugs Became 2026 Attack Infrastructure
First seen in March 2026, AryStinger turns unpatched, end-of-life routers and NAS devices into a covert reconnaissance network.
Greg Allen
Share this post via:
Security
Aug 25, 2026
CVE-2026-59270: Spring Security Embedded LDAP Admin DN Exposure
How an embedded UnboundID test server binds to every network interface with a well-known admin credential, letting anyone who can reach the port read or rewrite the directory.
Greg Allen
Share this post via:
Compliance
Aug 24, 2026
Cyber Insurance and End-of-Life Software: What's Excluded in 2026
Navigating the Shift from Record-Keeping to Underwriting: How EOL Software Impacts Your Policy Coverage in 2026SEO Meta Description
Greg Allen
Share this post via:
Security
Aug 21, 2026
CVE-2026-27601 & CVE-2021-23358: Underscore.js DoS and Template Code Injection
How two unguarded inputs to Underscore.js internals, an unbounded recursion depth, and an unvalidated template variable name, let remote data crash a Node.js process or run attacker-chosen code.
Ryan Jasinski
Share this post via: